Runtime Isolation Depth Benchmarks for Agent Execution Platforms Below the Syscall Layer
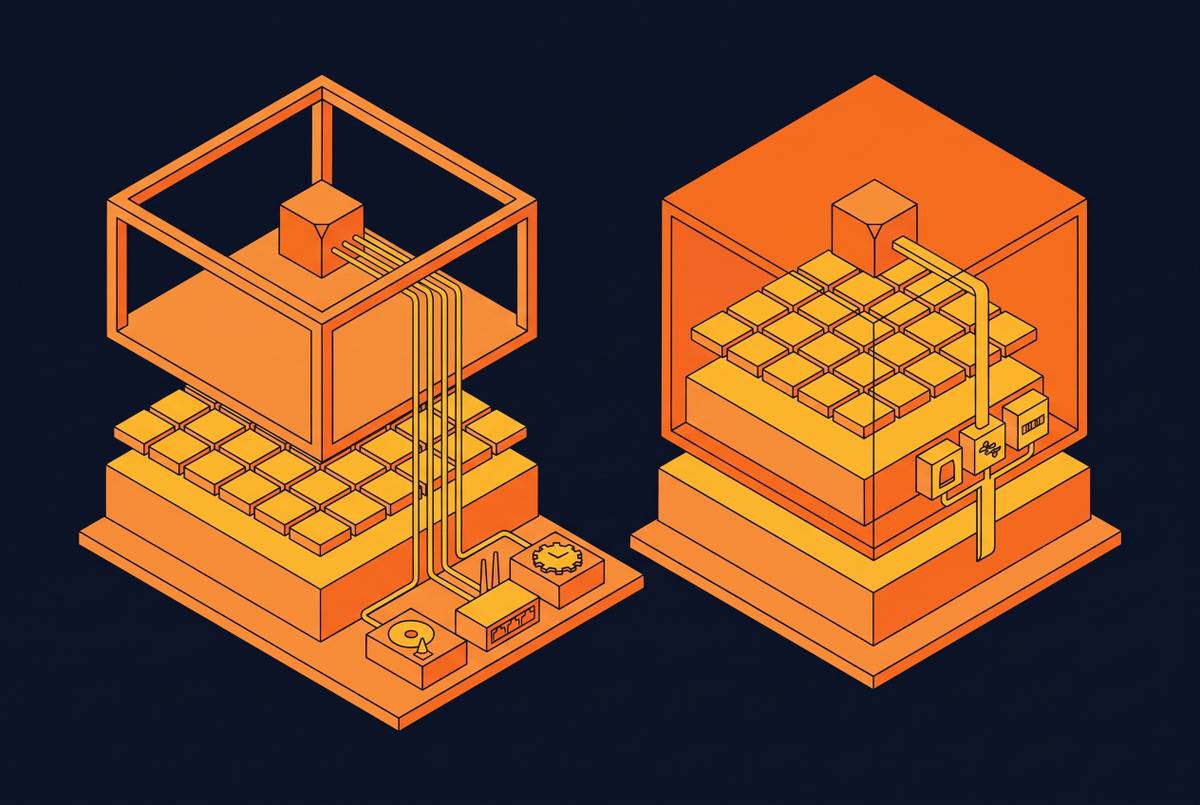
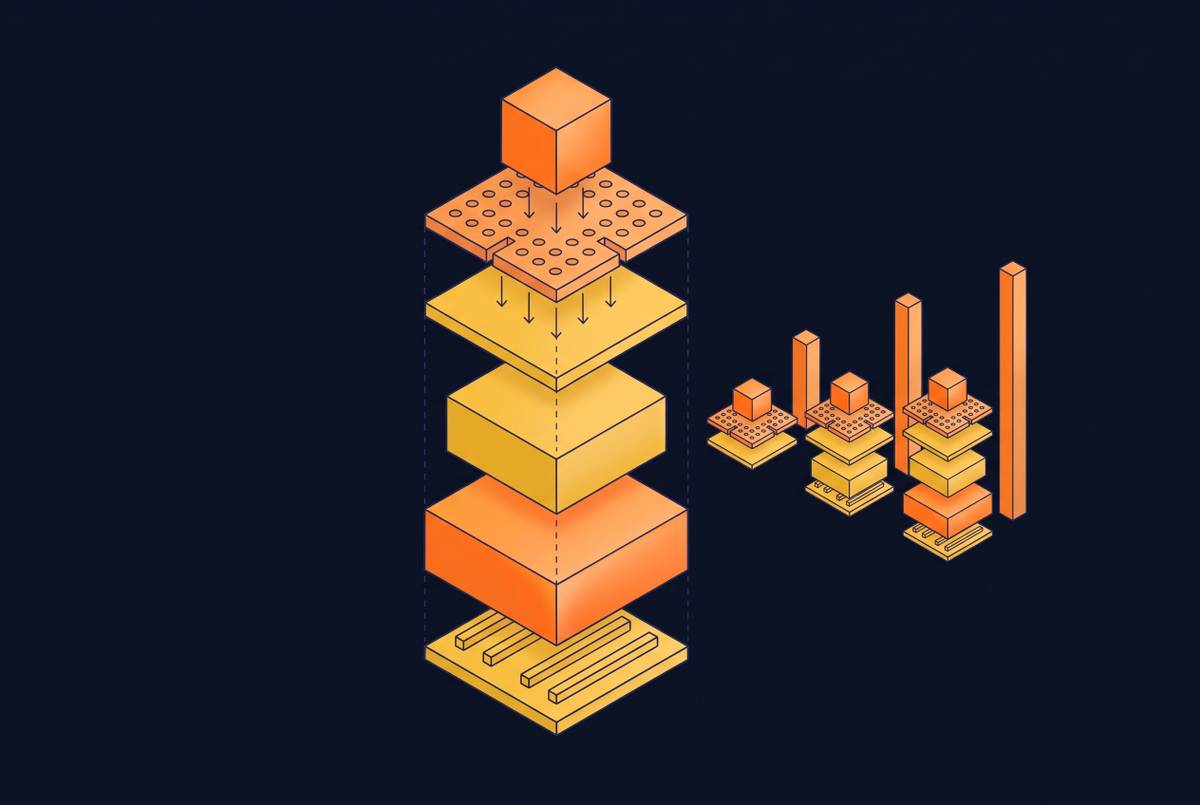
Containers, gVisor, and Firecracker differ most in how much kernel an agent shares.
Demarco Fitch
Section
17 stories in Sandbox & Runtime.
Containers, gVisor, and Firecracker differ most in how much kernel an agent shares.
Firecracker gives each agent its own kernel; containers share one.
Four shared-infrastructure risks that session isolation alone cannot stop.
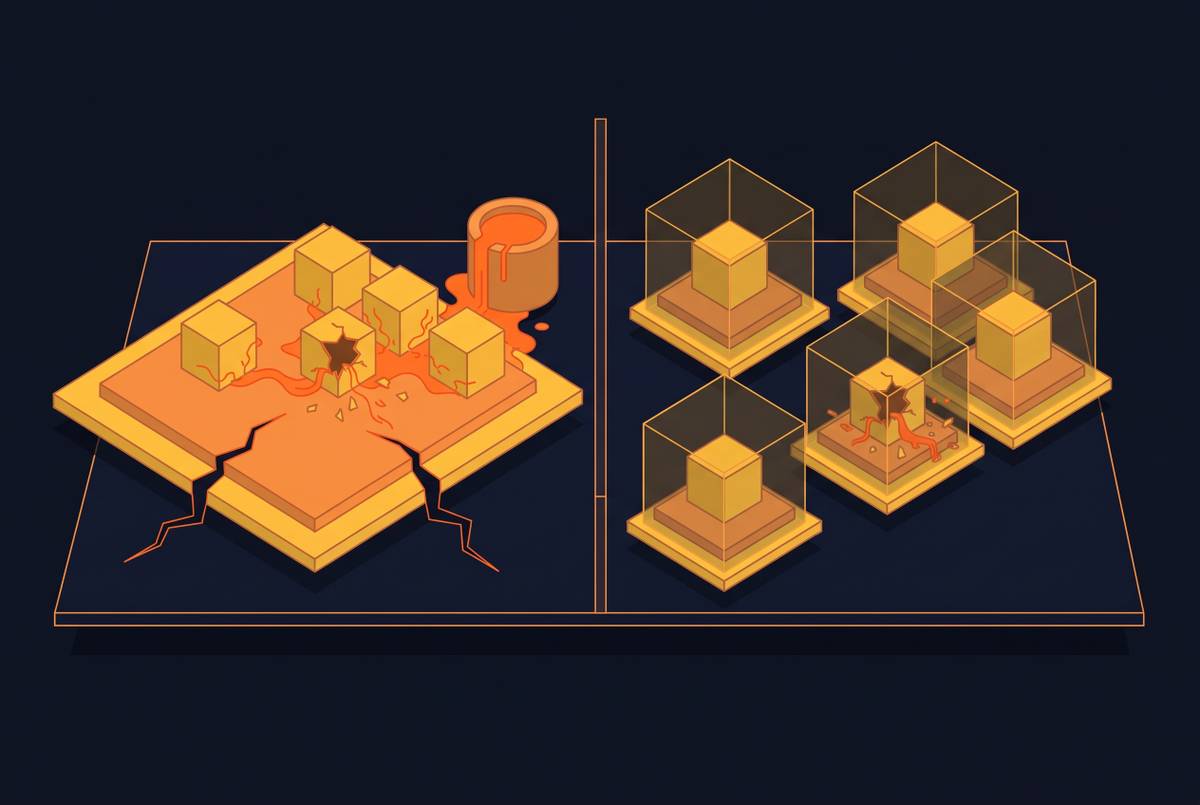
Firecracker microVMs give each agent its own kernel, and 2026's kernel escapes show why.
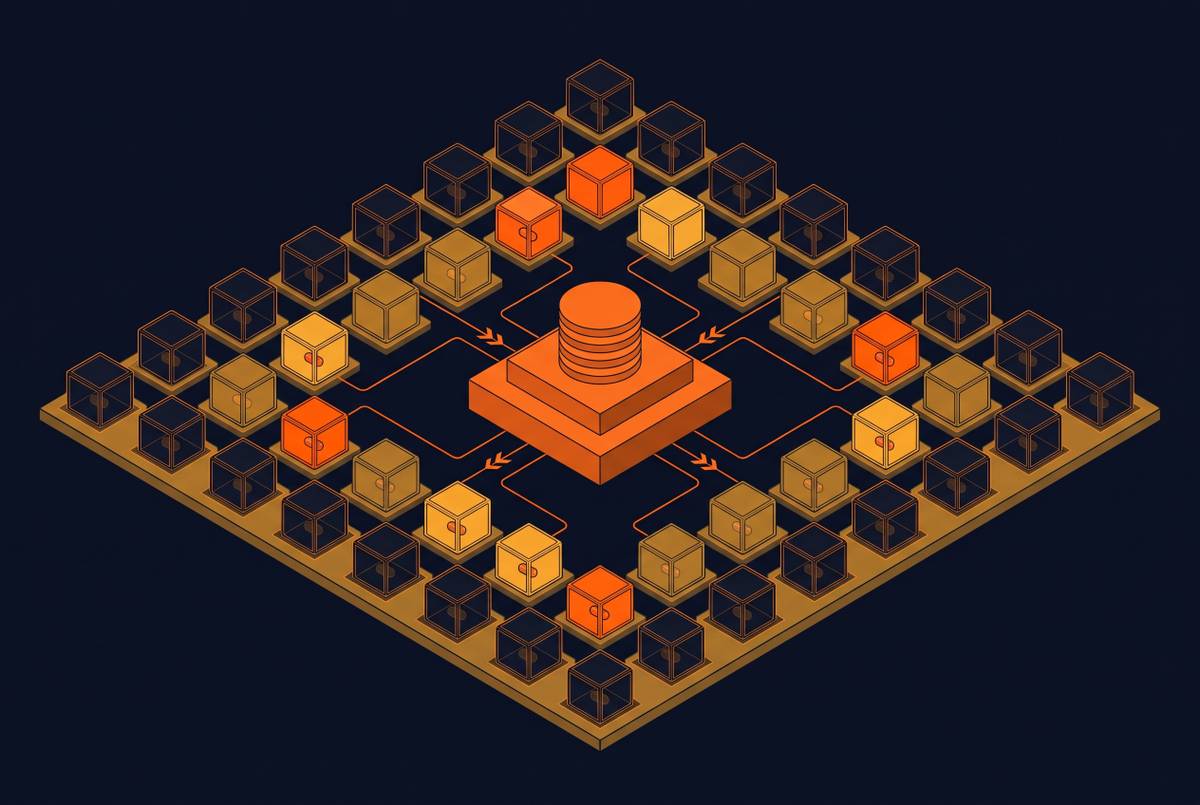
Scheduler design, not raw capacity, sustains hundreds of isolated AI agents.
Firecracker isolates agent kernels but leaves host, egress, and storage gaps uncovered.
Persistent AI agents need stateful runtimes, not ephemeral functions designed for stateless work.
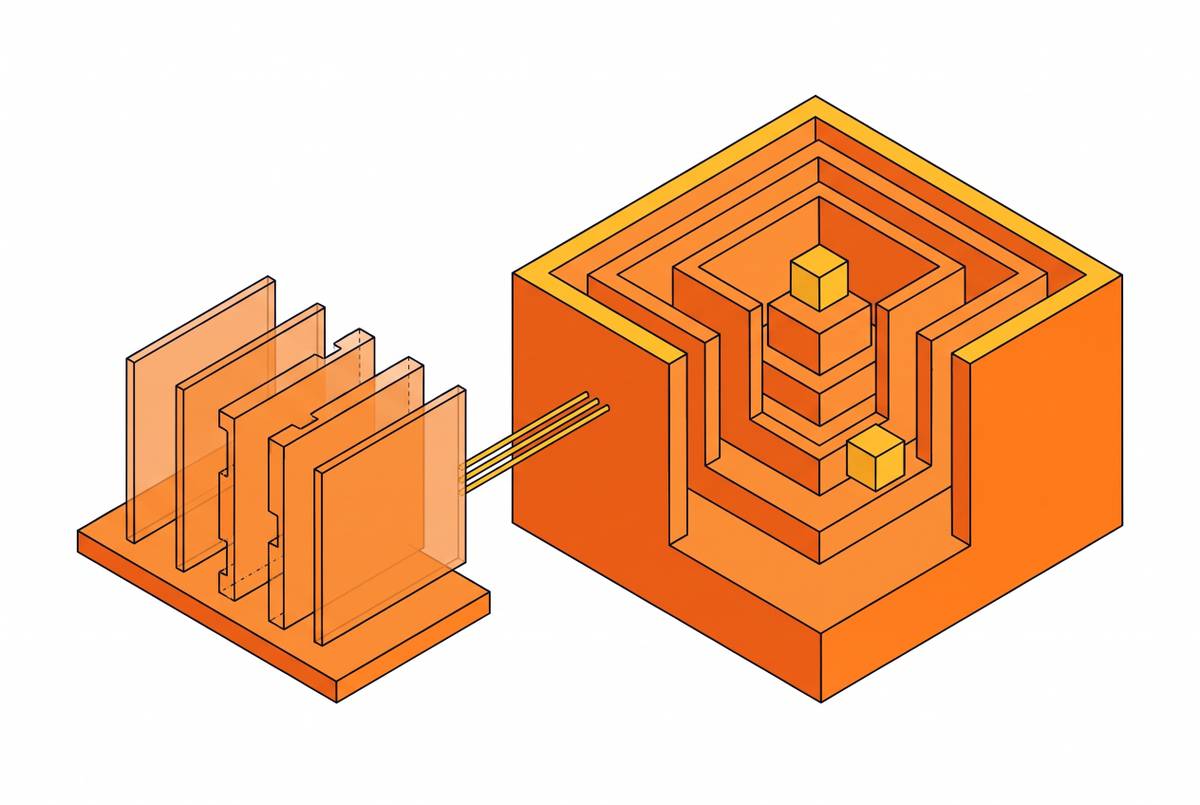
Micro-VM isolation provides the kernel boundary that containers cannot offer hostile agent code.
Firecracker boots each agent with its own isolated kernel instead of sharing the host's.
Kernel vulnerabilities in one tenant can escape shared containers but not per-agent microVMs.
Firecracker microVMs restore in milliseconds while QEMU and cloud VMs lag behind.
Wasm isolates through runtime sandboxing; micro-VMs isolate through hardware virtualization.
Hardware-enforced VM isolation is now essential for multi-tenant browser agent security.
Firecracker trades operational complexity for stronger isolation than gVisor's software approach.
Agents need persistent state; serverless destroys it between every invocation.
Containers share a kernel with the host, and micro-VMs don't.