Linux Cgroups V2 Memory Limits for Agent Processes
Cgroup v2 memory controls let teams right-size agent sandboxes for unpredictable peaks.
Priya Venkataraman
Cgroup v2 memory controls let teams right-size agent sandboxes for unpredictable peaks.
Proper scope design prevents agents from accessing unrelated tools even with valid tokens.
New transport design eliminates sessions for simpler HTTP deployment.
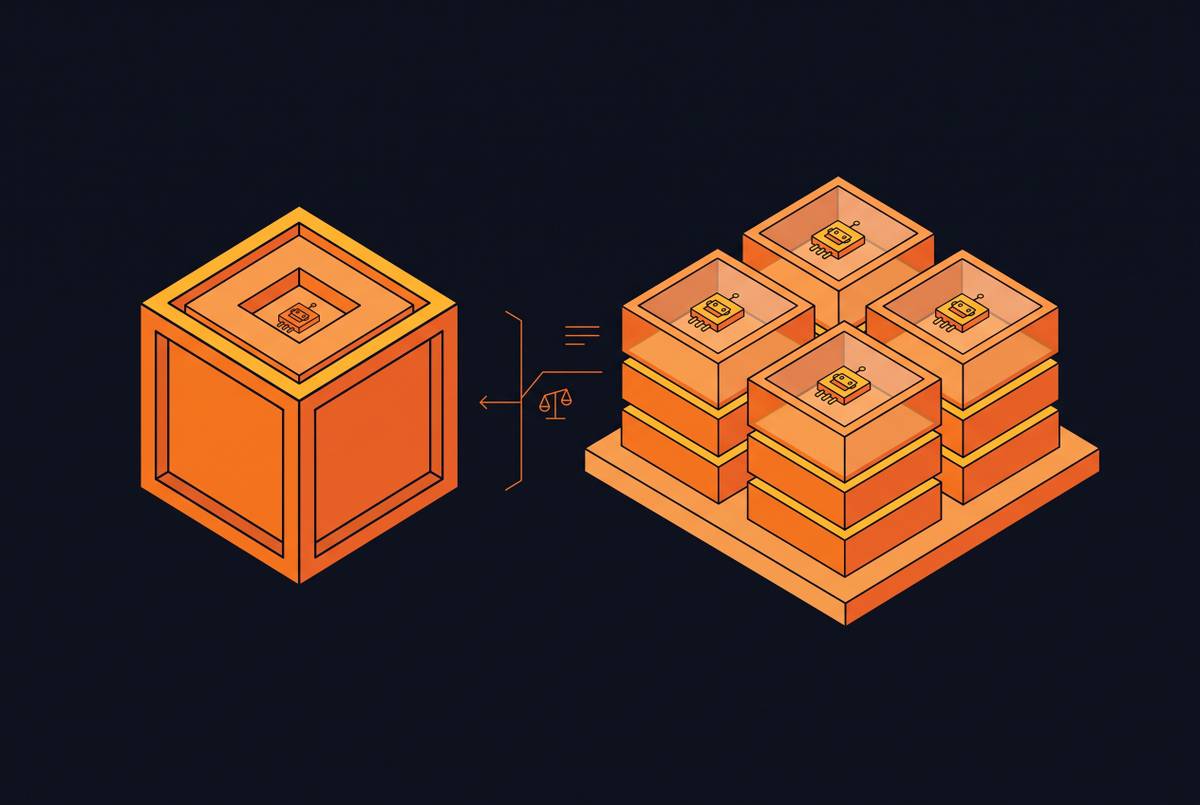
Kernel vulnerabilities in one tenant can escape shared containers but not per-agent microVMs.
Firecracker microVMs restore in milliseconds while QEMU and cloud VMs lag behind.
Wasm isolates through runtime sandboxing; micro-VMs isolate through hardware virtualization.
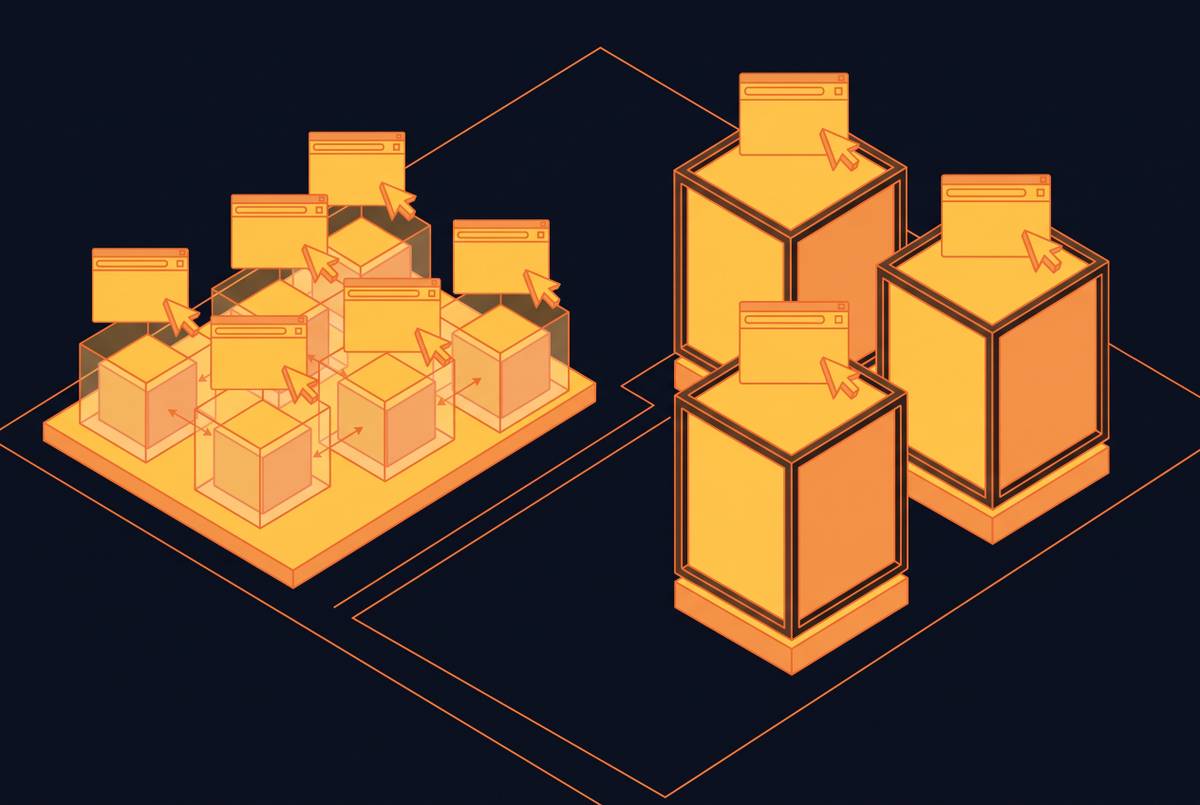
Hardware-enforced VM isolation is now essential for multi-tenant browser agent security.
Firecracker trades operational complexity for stronger isolation than gVisor's software approach.
Agents need persistent state; serverless destroys it between every invocation.
Containers share a kernel with the host, and micro-VMs don't.